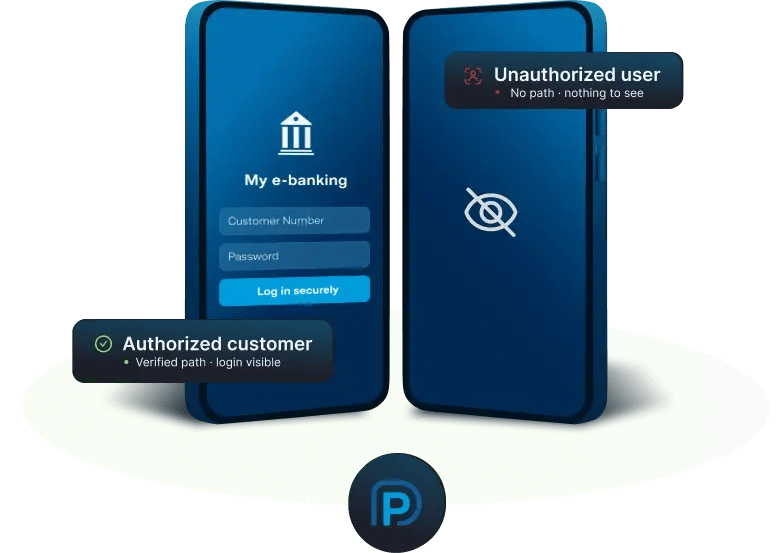



The application is placed behind Anapaya EDGE, on premises or in the cloud, with a PathGuard Gateway in front of it. The gateway terminates
the connection, acting as a VPN termination
point or an HTTP reverse proxy, so the
application backend itself does not need to
be modified.

Applications and APIs
Partner API integrations and customer applications, connected through the SCION SDK so the link between device and backend is SCION end to end.
-
E-banking
-
EV chagring
- Patient portal

Web services
The Citizen and supplier portals, protected through the PathGuard Web SDK, with no software for the user to install.
-
Telemedicine
-
Payment gateway
-
Ecommerce

Remote access
Operational and IoT connectivity, protected through the PathGuard VPN client without changing the applications behind it.
-
VPN
-
Micro-branch communication
-
Field devices